Last reviewed: 6 October 2026
Security and delivery controls embedded in the operating model.
This page describes the controls YottaLyte applies or is formalising for client data, production access, software delivery and team lifecycle. Formal assurance is treated as an extension of operating maturity rather than a substitute for it.
Where do you store our data?
Client data should remain in approved customer or project-specific environments wherever practical. Storage location, retention, encryption, backups and transfer requirements are defined per engagement. Data is not to be copied into personal storage or unrelated client environments.
Can your engineers access production?
Only when the engagement requires it and the client authorises it. Access should be least-privilege, attributable, time-bounded where practical and removed when no longer needed. Customer environments stay logically segregated.
How do you ship software safely?
Requirements and architecture precede implementation. Code is version-controlled, reviewed, validated and deployed through controlled environments. Production-impacting changes should have peer review, test evidence and post-deployment verification.
How do you manage credentials?
Secrets belong in approved credential-management systems, not source code, chat, personal notes or plaintext project files. Access should be role-based and rotated or revoked when exposure risk or team changes require it.
Do you perform code reviews?
Yes as the standard path for production-impacting changes. Reviews should consider correctness, maintainability, security, operability and the architecture contract—not just formatting.
What happens when someone leaves?
Company and client access should be revoked promptly, devices and credentials accounted for, and secrets rotated where appropriate. Access rights should also be reviewed when roles change.
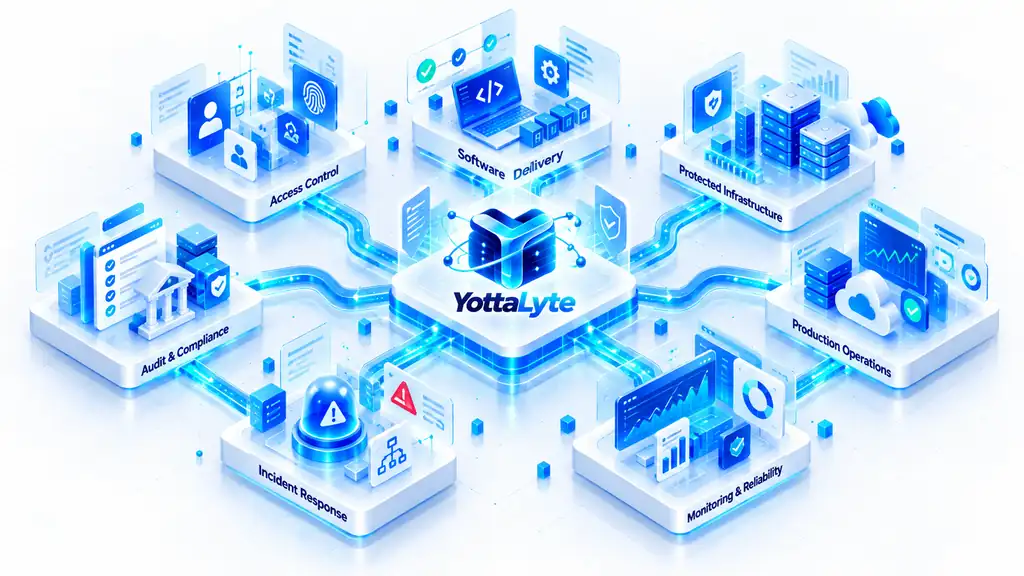
Control framework supporting delivery governance.
Controls are formalised progressively as delivery maturity, client requirements and assurance obligations evolve.
NDA · MSA · SOW · DPA
Clear scope, confidentiality, data handling, ownership and commercial boundaries.
SDLC · review · release
Consistent development, review, validation, deployment and handover practices.
Access · secrets · devices
Least privilege, client segregation, credential controls and endpoint hygiene.
Incident · backup · BCP
Prepared response, recovery expectations and continuity procedures.
Formal assurance aligned to operating maturity and client requirements.
SOC 2 or ISO 27001 readiness will be evaluated against customer requirements, operating maturity and the commercial case for certification.